
📊 Full opportunity report: Active Threats In 2026: CVE-2026-8037 And LoadMaster Command Injection Attacks on IdeaNavigator AI — validation score, market gap, and execution plan.

Turn your quiet moments into listening time
- Thousands of audiobooks, podcasts and originals
- Listen on your phone, tablet or Echo — also offline
- Cancel anytime
TL;DR
Security researchers confirm that CVE-2026-8037, a command injection vulnerability in Progress LoadMaster, is being actively exploited by threat actors. This development raises urgent concerns for organizations using affected systems. Details on the scope and mitigation are still emerging.
Cybersecurity officials have confirmed that CVE-2026-8037, a command injection vulnerability in Progress LoadMaster, is actively being exploited by malicious actors in 2026. This marks a significant escalation, as organizations using LoadMaster devices face immediate risk of compromise, data breaches, and service disruptions.
According to cybersecurity sources, multiple threat groups are exploiting CVE-2026-8037, which was publicly disclosed earlier this year. The vulnerability allows attackers to execute arbitrary commands on affected LoadMaster appliances, which are widely used for load balancing and application delivery. The exploitation was first detected by security monitoring firms and has since been confirmed by government agencies.
Security experts emphasize that the attack technique involves sending specially crafted requests to vulnerable LoadMaster systems, enabling remote code execution. While the full scope of affected versions remains under investigation, early reports suggest that many organizations using outdated or unpatched LoadMaster firmware are at risk. No comprehensive patch has been publicly released yet, though Progress Software has acknowledged the issue and is working on mitigation guidance.
Implications for Organizations Using LoadMaster Devices
This active exploitation of CVE-2026-8037 presents a pressing threat to organizations relying on LoadMaster for network traffic management. Successful attacks can lead to remote code execution, data theft, service outages, and potential lateral movement within networks. Organizations that have not yet applied security updates or mitigations are at heightened risk, making this a critical incident for cybersecurity teams to address immediately.
As an affiliate, we earn on qualifying purchases.
Background on CVE-2026-8037 and LoadMaster Vulnerabilities
CVE-2026-8037 was publicly disclosed in early 2026, with initial security analyses indicating a command injection flaw in certain versions of Progress LoadMaster appliances. The vulnerability was identified through routine security testing and reported to Progress Software, which classified it as a high-severity issue. Since then, threat actors have rapidly developed exploits, with cybersecurity agencies issuing alerts about active campaigns targeting vulnerable systems.
LoadMaster devices are widely deployed in enterprise and small-to-mid-sized organizations for load balancing and application delivery. The widespread use of these devices, combined with delayed patching, has created a fertile ground for exploitation. Prior to this, LoadMaster vulnerabilities have historically been exploited in targeted attacks, but the current activity marks a significant escalation in threat level.
“We are seeing active exploitation of CVE-2026-8037, with threat actors leveraging it for remote code execution in real-world attacks.”
— an anonymous cybersecurity researcher
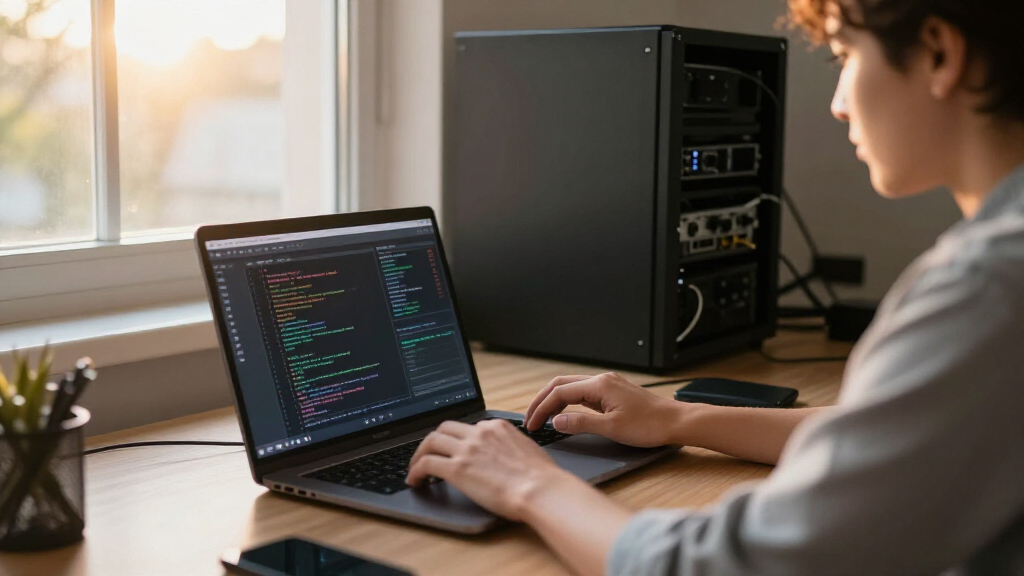
network load balancer security device
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Extent and Impact of the Current Exploitation Campaigns
While exploitation has been confirmed, the full scope of impacted organizations, specific threat actors involved, and the extent of data compromised remain unclear. Researchers are still analyzing attack patterns and identifying affected systems, but detailed attribution and impact assessments are ongoing.
enterprise load balancing appliances
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Expected Security Updates and Mitigation Measures
Progress Software is expected to release official patches and security advisories shortly. In the meantime, organizations are advised to disable vulnerable services, implement network segmentation, and monitor for signs of compromise. Cybersecurity teams should stay alert for further updates and prepare incident response plans tailored to LoadMaster-related threats.
cybersecurity threat detection tools
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Key Questions
What is CVE-2026-8037?
CVE-2026-8037 is a command injection vulnerability in Progress LoadMaster appliances that allows remote attackers to execute arbitrary commands.
How are threat actors exploiting this vulnerability?
Attackers are sending specially crafted requests to vulnerable LoadMaster devices, enabling remote code execution and potential control over affected systems.
What should organizations do now?
Organizations should apply available patches, disable vulnerable services, and monitor network traffic for suspicious activity.
Are all LoadMaster devices affected?
Not all devices are affected; impact depends on the version and configuration. Organizations should verify their systems against vendor advisories.
What are the potential consequences of exploitation?
Successful exploitation can lead to data breaches, service outages, and lateral movement within networks, increasing overall security risk.
Source: IdeaNavigator AI
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.